LRLucas Rocha
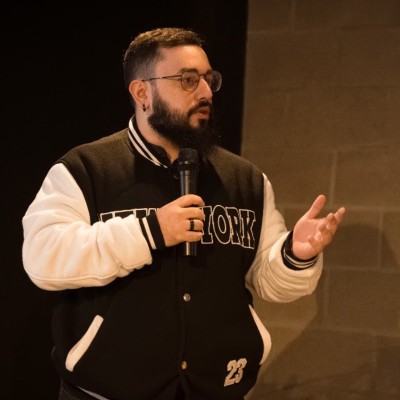
Lucas Rocha speaking into a microphone

Engineering Manager · AppSec

I build security
into software
systems.

Engineering manager with 10+ years in software engineering. I lead teams, build secure development practices and turn application risks into practical engineering work.

10+years in software engineering
2024AppSec consulting started
3public security labs
WritingCyber Coffee newsletter

Security Labs

Built to understand. Documented to share.

Explore all labs

Independent security experiments. Public code and documented evidence.

Defensive security lab

Posto de Observação

An isolated Cowrie honeypot and Suricata IDS lab, with Alloy, Loki and Grafana for log collection and analysis.

  • Cowrie
  • Suricata
  • Grafana

Mobile security lab

Android ContentProvider Exposure

An educational InsecureShop lab exploring ContentProvider permissions, APK analysis with JADX and a separate Kotlin app to demonstrate unintended data access in a controlled Android emulator.

  • Android
  • Kotlin
  • JADX
  • InsecureShop

Open source

Contributing beyond my own code.

More on GitHub

Contributions to tools used by the security community, with the changes and review history open for everyone.

ProjectDiscoverynuclei-templates
Merged

Detection engineering · PR #17027

Detecting exposed panels and APIs

Added detection templates for Chatwoot, Directus, Grafana Loki and VictoriaMetrics vmagent. Refined matchers and removed duplicate templates during maintainer review.

  • Nuclei
  • YAML
  • Security detection
What this contribution covers
  • Chatwoot: detection of an exposed Super Admin login panel.
  • Directus: detection of API metadata accessible without authentication.
  • Grafana Loki: detection of exposed log stream labels.
  • VictoriaMetrics vmagent: detection of an exposed targets API.

Cyber Coffee · Writing

AppSec, with context.

View all editions

Prompt Injection Has No Patch — And That's Why It Changes Product Design

Prompt injection cannot be patched because LLMs cannot separate data from instructions. True defense requires architecture outside the model: least privilege, treating output as untrusted, and human approval for irreversible actions.

  • Prompt Injection
  • LLM Security
  • Application Security

About

Security is built by people.

More about me

Technical depth.
Practical solutions.
Lasting impact.

I’m an engineering manager specializing in Application Security. My background spans infrastructure, full-stack and mobile development, frontend architecture and technical leadership. I work across engineering and security: threat modeling, secure development, vulnerability management and mentoring teams.

  • Security
  • Automation
  • Cloud
  • Leadership
  • Open Source
  • AI
  1. Engineering Security Manager · Trinca

    Engineering leadership, secure development practices and coordination across software, AI and cybersecurity.

  2. Application Security Specialist · Independent

    Threat modeling with STRIDE/DREAD, automated security testing, vulnerability reporting and secure-development training.

  3. Tech Lead · CRMBonus

    Technical leadership and security champion work across frontend, backend, mobile and QA; engineering standards and mentoring.

  4. Engineering Lead · Porto

    Frontend chapter leadership, React/AEM architecture, testing, observability and engineering practices.

Earlier experience · 2014–2022
  1. Frontend Staff Engineer · Árvore

    Frontend quality, maintainability and WCAG accessibility.

  2. Tech Manager · BeCapital

    Engineering management, technical delivery and secure-development practices.

  3. Senior Software Engineer · BeCapital

    Software architecture, investment platforms, automation and cloud services.

  4. Full Stack Developer · Stone Co.

    Web and mobile systems, architecture, testing and accessibility.

  5. Mobile Developer · Target Bank

    Migration from native Android/Java to Flutter, mobile architecture and accessibility.

  6. Full Stack Developer · TV Escola

    Closed-caption and broadcast engineering systems, documentation and accessibility.

  7. Jr. DevOps Engineer · TV Escola

    Infrastructure, virtualization, monitoring, cloud backups and service availability.

View full experience

Technologies

The tools behind the work.

Aikido
OWASP Threat Dragon
Python
Azure
Docker
GitHub
Datadog
SonarCloud
OWASP ZAP
Semgrep
Trivy
Gitleaks
Wazuh
DefectDojo
Linux
Cowrie
Suricata
Grafana
Loki

Let’s talk

Build safer.
Build together.

Let’s talk about application security, engineering leadership, secure development or a technical collaboration.

LR

Find your way.

Esc to close · Tab to navigate · Enter to open